Loading...

Why BFSI Software Projects Blow Past Budget (And What We Do Differently at Speqto)

Every fintech founder or BFSI IT head has heard some version of this line at least once: “We’re 60% over budget, and we’re still not live.” It’s such a common story that most people assume it’s just how software works. It isn’t. In our years of building lending platforms, KYC systems, and payment gateways, we’ve seen the same five or six mistakes repeat themselves across projects worth ₹15 lakhs and projects worth ₹5 crores. The scale changes. The mistakes don’t.

This post is about what actually causes budget overruns in BFSI and fintech software projects — not the textbook answer, but what we’ve watched happen on real engagements — and the specific things that keep a project’s spend honest.

1. Requirements that are “mostly” defined

A payments startup once came to us with a fairly detailed PRD for a UPI reconciliation dashboard. Detailed, except for one line: “settlement logic to be finalized with the bank partner.” That one open item meant three rounds of rework after the bank’s integration team shared their actual file format — six weeks after development had already started on assumptions.

In BFSI specifically, requirements are rarely “internal-only.” They depend on a bank, an NBFC partner, a payment aggregator, or a regulator’s circular. If those dependencies aren’t nailed down before coding starts, you’re not building software — you’re building a guess.

2. Compliance surfaces late, not early

We’ve seen teams build an entire loan origination flow and only bring in the compliance officer at UAT stage. That’s when someone points out the audit trail doesn’t capture consent timestamps the way the RBI’s digital lending guidelines require. Now you’re not adding a feature — you’re re-architecting a module that touches five other services.

Compliance in BFSI isn’t a checklist you run at the end. It changes data models, logging, retention periods, and even API contracts. Every rupee saved by skipping early compliance review gets spent three times over in rework later.

3. Change requests without a cost conversation

This is the quiet budget killer. A client asks, “Can we also add a co-lending split logic while you’re in there?” It sounds small. Nobody stops to ask what it touches — the disbursement engine, the reporting layer, the partner reconciliation reports. Three “small asks” later, you’ve added six weeks of work with no corresponding change in timeline or budget expectations.

We had an NBFC client where four such “quick additions” over two months added more scope than the original SRS. None were individually unreasonable. Collectively, they doubled the build.

4. Estimation based on hope, not history

A lot of estimates are built by asking, “How long should this take?” instead of “How long has this actually taken before?” KYC integrations with third-party providers like Aadhaar eSign or CKYC almost always take longer than the API documentation suggests, because sandbox behavior and production behavior differ. If your estimate doesn’t build in that gap, you’re already behind before the sprint starts.

5. No one owns the budget conversation day to day

On fixed-price projects with weak governance, the vendor absorbs scope creep quietly to avoid conflict — until margins are gone and quality drops. On time-and-material projects without a dedicated owner tracking burn versus progress, the client discovers the overrun only when the invoice arrives. Either way, the damage is already done by the time anyone notices.

What actually works

  • Run a paid discovery sprint before quoting a final number. Two to three weeks to map data flows, partner dependencies, and compliance touchpoints costs far less than discovering gaps mid-build. On a recent digital lending platform, discovery surfaced a co-lending reconciliation requirement that would have added 25% to the budget if found in month three instead of week two.
  • Bring compliance and security review in at the design stage, not the testing stage. For BFSI, this means a compliance sign-off checkpoint before development starts on any module touching customer data, consent, or money movement.
  • Price change requests in real time, not at project close. Every new ask gets a one-page impact note — effort, cost, timeline shift — signed off before work starts. This alone has cut scope-driven overruns by more than half on our recent engagements.
  • Estimate from historical data, not documentation. We keep effort logs from past BFSI integrations (CKYC, NPCI, payment gateways) and use actual timelines, not vendor-promised SLAs, to build estimates.
  • Assign a single owner to track budget burn weekly, not monthly. Weekly visibility means a 10% drift gets caught and corrected. Monthly visibility means you find out after it’s a 40% drift.

The real lesson

Budget overruns in BFSI software rarely come from bad developers or bad tools. They come from unclear dependencies, late compliance checks, and scope changes nobody costed properly. Fix those three, and most of the “software projects always go over budget” problem disappears on its own.

At Speqto, we’ve built our delivery process around exactly these checkpoints — not because it sounds good in a proposal, but because we’ve watched what happens when they’re skipped. If you’re scoping a BFSI or fintech build right now and want a second opinion on where the budget risk actually sits, that’s a conversation worth having before the SOW is signed, not after.

RECENT POSTS

Reducing Loan Processing Time Through Workflow Automation: What Actually Works

If you’ve spent any time in lending operations, you already know the real cost of a slow loan cycle isn’t just customer frustration — it’s lost business. A borrower who waits 10 days for approval has usually applied with two other lenders in the meantime. We’ve seen this play out repeatedly with our BFSI clients […]
How to Plan a Phased ERP or CRM Implementation Without Breaking What Already Works

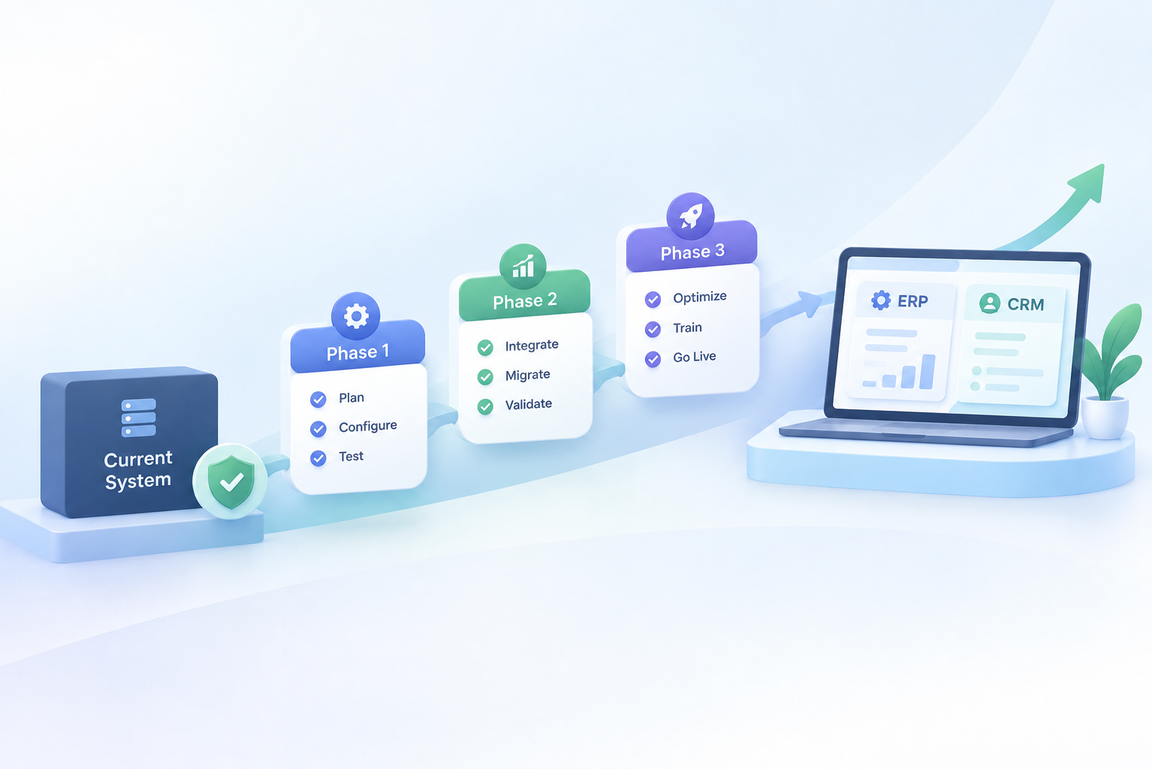
Every BFSI or fintech leader we’ve worked with has heard the same horror story at least once — a bank or NBFC switches on a new core system overnight, and for three weeks nobody can process loan disbursements properly. That’s the risk of a “big-bang” ERP or CRM rollout, and it’s exactly why phased implementation […]

Why Microservices Architecture Reduces Long-Term Maintenance Cost (A BFSI Perspective)

Every BFSI and fintech leader we’ve worked with at Speqto Technologies eventually asks us the same question: “Our monolith works fine today, so why should we spend money breaking it apart?” Fair question. The honest answer is — you shouldn’t do it for today. You do it for the three years after today, when your […]

Building Customer-Facing Portals for Financial Institutions: What Actually Works

Over the last few years, our team at Speqto Technologies has built portals for NBFCs, cooperative banks, insurance brokers, and a couple of wealth management firms. One thing that keeps surprising clients: the hardest part is rarely the UI. It’s getting core banking integrations, compliance workflows, and support escalation to work together without the whole […]

How AI Can Improve Fraud Detection in Banking Systems: What Actually Works

Most banks we talk to aren’t short on fraud rules. They have hundreds of them — thresholds on transaction amount, geography mismatches, velocity checks, blacklisted IFSC codes. The problem isn’t the lack of rules; it’s that fraudsters have learned to operate just below every threshold. That’s where AI earns its place, not as a buzzword, […]

POPULAR TAG

POPULAR CATEGORIES