Loading...

Data Security Compliance Checklist for BFSI Software Vendors: What Actually Matters in 2026

A few months back, one of our clients — a mid-sized NBFC lending platform — almost lost a bank partnership deal because their vendor risk assessment flagged “insufficient encryption key rotation policy” during due diligence. Two weeks of scrambling, a rushed audit, and a very uncomfortable board call later, the deal went through. But it shouldn’t have been that close.

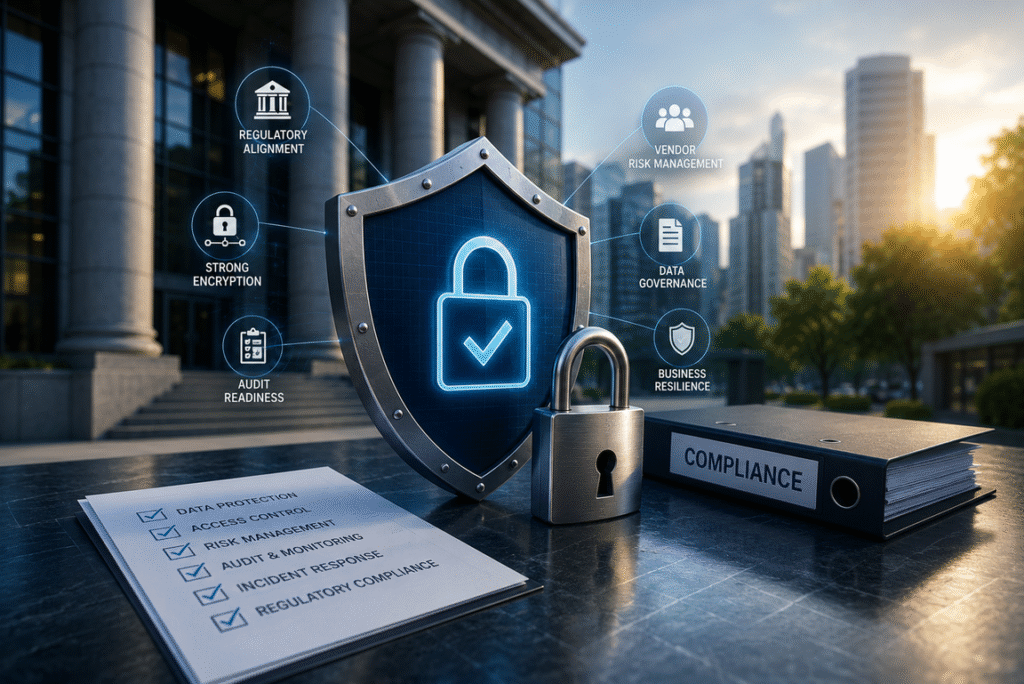
This is the reality for most BFSI software vendors today. You can build a brilliant lending engine, a slick payments dashboard, or a smart claims processing tool — but if your data security posture isn’t audit-ready, banks, NBFCs, and insurers simply won’t sign the contract. At Speqto Technologies, we’ve built and hardened software for fintech and BFSI clients long enough to know that compliance isn’t a one-time checkbox exercise. It’s an ongoing discipline. Here’s the checklist we actually use with our clients.

1. Map Your Data Against Actual Regulations, Not Assumptions

Most vendors assume “we’re ISO 27001 certified, we’re good.” That’s a start, not an answer. If you’re serving Indian BFSI clients, you need to be aligned with:

  • RBI’s Cyber Security Framework for banks and NBFCs, including outsourcing guidelines under the IT Outsourcing Master Direction.
  • SEBI’s Cybersecurity and Cyber Resilience Framework (CSCRF) if you’re working with brokers, AMCs, or market infrastructure institutions.
  • IRDAI’s Information and Cyber Security Guidelines if your client is an insurer.
  • The Digital Personal Data Protection (DPDP) Act, 2023 — which now applies regardless of sector, and changes how consent, breach notification, and data localization are handled.

We had a payments-adjacent client who assumed PCI DSS covered everything. It didn’t cover their obligations under RBI’s outsourcing norms around subcontractor disclosure. That gap alone delayed onboarding by six weeks.

2. Encryption Isn’t Optional — But Key Management Is Where Vendors Fail

  • AES-256 encryption at rest, TLS 1.2+ in transit — table stakes at this point.
  • Document your key rotation schedule (90 days is a common ask from bank auditors).
  • Use a proper HSM or KMS (AWS KMS, Azure Key Vault) instead of hardcoding keys or storing them in config files — we still see this in legacy fintech codebases more often than you’d expect.
  • Encrypt PII fields individually (Aadhaar, PAN, account numbers) rather than relying on database-level encryption alone.

3. Access Control That Can Survive an Audit

  • Role-based access control (RBAC) with documented approval workflows — not just “who has admin rights” but “why do they have it.”
  • Mandatory MFA for anyone touching production data, including your own dev team.
  • Quarterly access reviews. One insurance-tech client of ours found three former employees still had staging environment access during a routine review — nothing malicious happened, but it’s exactly the kind of finding that fails an IRDAI audit.
  • Just-in-time access for support engineers instead of standing production credentials.

4. Audit Trails That Are Actually Usable

Logging everything is easy. Making logs useful for an auditor or a forensic investigation is harder. Your system should be able to answer, within minutes: who accessed this customer’s data, when, and why. We built a centralized audit logging layer for a lending client using immutable log storage (write-once) specifically because their bank partner’s compliance team asked for tamper-proof logs during onboarding — not just logs.

5. Vendor and Sub-Processor Risk — Your Blind Spot

  • List every third-party service touching customer data — cloud provider, SMS gateway, KYC verification API, analytics tools.
  • Get security certifications (SOC 2, ISO 27001) from each sub-processor, not just yourself.
  • Have a documented data processing agreement with each one, mapped to DPDP Act requirements on cross-border transfer.

This one trips up more vendors than anything else. You can be perfectly compliant internally and still fail an audit because your OTP vendor stores data on servers outside India without disclosure.

6. Incident Response Plan — Written, Tested, Not Theoretical

  • A documented breach notification timeline (CERT-In mandates reporting within 6 hours of becoming aware of certain incidents — this is non-negotiable and frequently missed).
  • A tested rollback and containment procedure, not just a policy document sitting in a shared drive.
  • Clear internal ownership — who calls the client, who calls the regulator, who talks to the press, if it comes to that.

7. Data Minimization and Retention Discipline

Stop collecting data “just in case.” One of the fastest wins we’ve implemented for clients is a retention policy that auto-purges KYC documents and transaction logs beyond the regulatory minimum. Less stored data means less breach exposure and a much shorter, calmer conversation during audits.

8. Employee and Vendor Security Training — Not Once a Year

Phishing simulations, secure coding training for developers, and quarterly refreshers for anyone with data access. Human error, not sophisticated hacking, is still the leading cause of BFSI data incidents.

Final Word

None of this is glamorous work, and that’s exactly why so many BFSI software vendors treat it as an afterthought — until a client’s compliance team sends back a 40-point questionnaire two days before a contract signing. Building security and compliance into your architecture from day one, rather than bolting it on before an audit, is the difference between winning enterprise BFSI clients and losing them at the finish line.

At Speqto Technologies, this checklist isn’t theoretical — it’s how we’ve helped fintech and BFSI clients get through vendor risk assessments without last-minute panic. If you’re building or scaling software for banks, NBFCs, or insurers, it’s worth an honest audit against this list before your next client review does it for you.

RECENT POSTS

The Real Cost of Delaying Digital Transformation: What Mid-Size BFSI Firms Are Losing Every Quarter

Every mid-size NBFC, cooperative bank, or insurance broker we’ve worked with at Speqto Technologies has, at some point, said some version of the same thing: “We’ll get to the digital overhaul next year, once things settle down.” The problem is, things never settle down. And the invoice for waiting keeps growing quietly in the background […]
How BFSI Companies Can Modernize Legacy Systems Without Disrupting Operations

Every BFSI leader we talk to at Speqto Technologies says some version of the same thing: “Our core system works, but it’s holding us back.” Then in the next breath: “But we can’t afford even four hours of downtime.” That tension between needing to modernize and being terrified of breaking something that processes millions of […]

7 Signs Your BFSI Business Needs a Digital Transformation Partner (Not Just Another IT Vendor)

Every BFSI leader we talk to has already “done” digital transformation in some form — a new CRM here, a mobile app there, maybe a chatbot bolted onto the website. Yet the same complaints keep surfacing: loan approvals still take days, reconciliation is manual, and the leadership team is making decisions off a spreadsheet someone […]

Why Custom Software Beats Off-the-Shelf Tools for Growing Businesses

A few months back, a mid-sized NBFC came to us at Speqto with a problem that’s more common than most people admit out loud: they had outgrown their loan management software, but nobody wanted to say it directly. Instead, the conversation was framed as “we need better reporting” or “the CRM feels slow.” Two calls […]

2027 Tech Trends BFSI and Fintech Companies Need to Start Preparing For Now

Every December, someone publishes a “top trends for next year” list, and most of it reads the same regardless of industry. We’re going to skip that exercise. At Speqto Technologies, we build and maintain systems for banks, NBFCs, insurers, and fintech startups, and what we’re seeing on the ground looks quite different from the generic […]

POPULAR TAG

POPULAR CATEGORIES